
Security Awareness Training Topics
Your people are one of the biggest assets in your security program. They are the control that notices when something feels off. But that only works if you tell them what to look for.
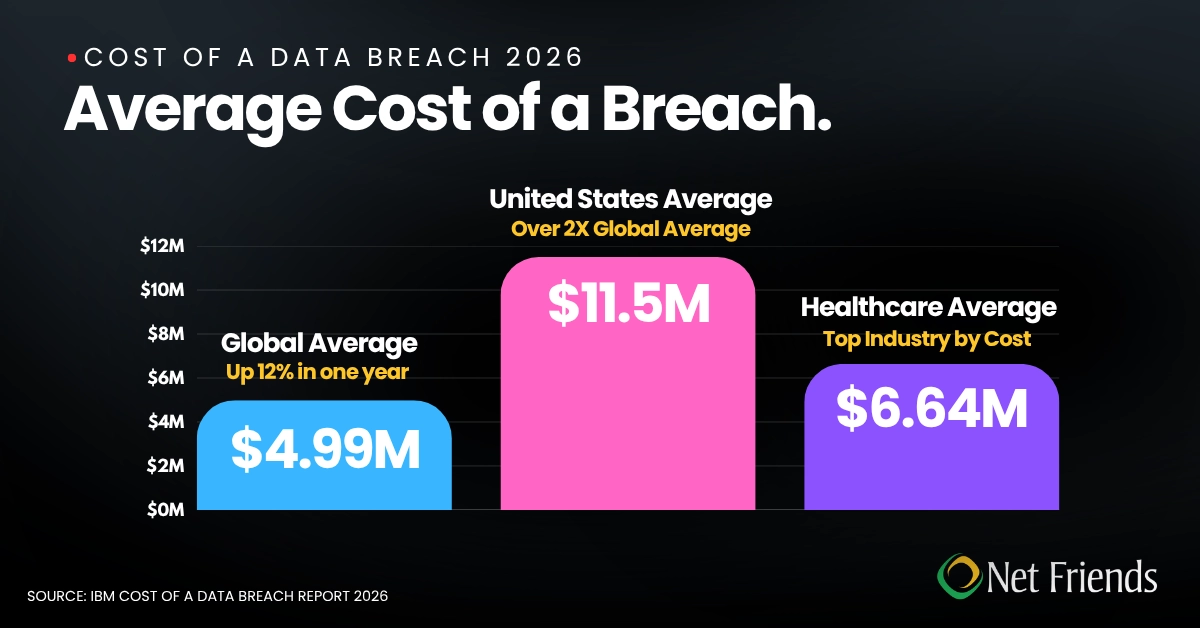
The numbers make the case better than we can. IBM's 2026 Cost of a Data Breach Report put the global average breach at a record $4.99 million, up 12% in a single year. In the United States, the average breach climbed to $11.5 million, more than double the global figure. Healthcare took the top industry spot for the thirteenth year, running at $6.64 million.
Here is the part that should shape your training plan. For the fourth consecutive year, phishing was the most common way attackers got in. Tools alone were never going to fix that, and no firewall has ever talked someone out of clicking a link.
What should your security awareness training program cover?
Start with the Ground You are Defending
Before you build a curriculum, it helps to name the territory. Most small and midsize organizations are protecting seven areas at once.
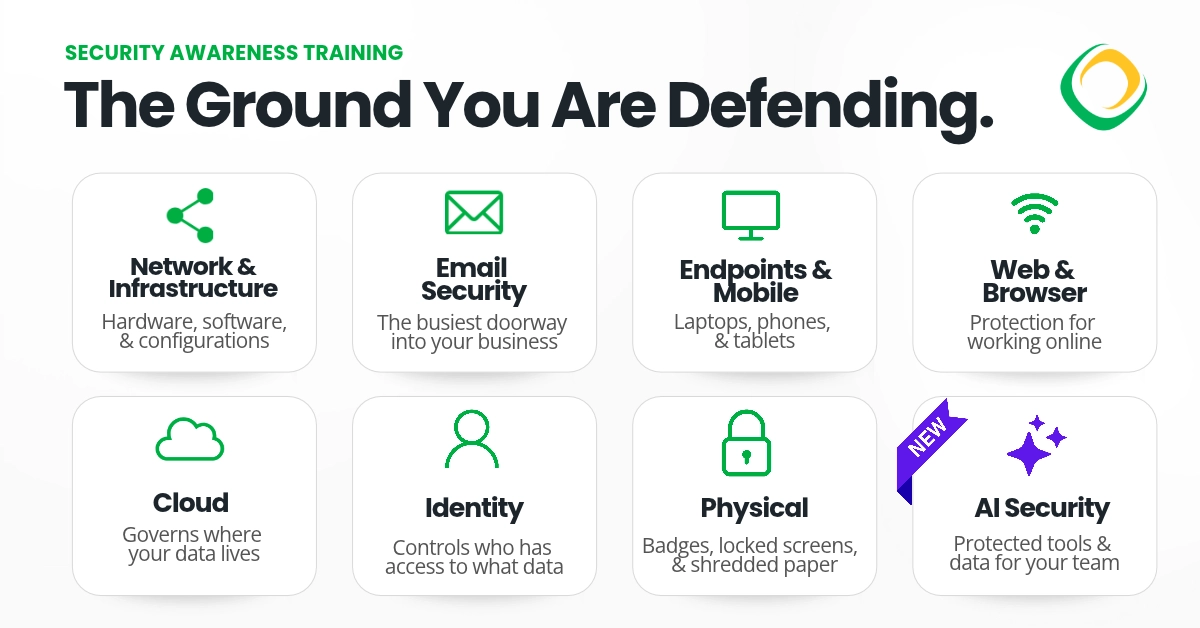
- Network and infrastructure security covers the hardware, software, and configurations that keep traffic and systems trustworthy.
- Email security protects the single busiest doorway into your business.
- Endpoint and mobile security cover laptops, phones, and tablets.
- Web and browser security protect people while they are working online.
- Cloud security governs the platforms where most of your data already lives.
- Identity security controls who is who and what they can reach.
- AI security, the newest addition to this list, governs how your team uses generative tools and what data goes into them.
Physical security still belongs in the conversation too. Badges, locked screens, shredded paper, and a healthy suspicion of strangers in the server room are not old fashioned.
Every one of these areas has a human component. That is where awareness training earns its keep.
Phishing and All the Variations
Phishing is still the headline act. IBM found it accounted for roughly 17% of breaches studied. Attackers send messages that look like they came from a bank, a vendor, a shipping company, or your own CEO, and ask the reader to click, download, or pay.
The methods of gaining access have grown and should also be included.
- Spear phishing targets one specific person with details pulled from LinkedIn and your website.
- Smishing arrives by text message, often about a delivery or a payroll change.
- Quishing hides the malicious link inside a QR code, which is exactly the kind of thing people scan without thinking.
- Business email compromise skips malware entirely and simply asks accounting to redirect a wire transfer.
Teach the tells. Urgency, an unexpected payment change, a sender address that is almost right, a link that does not match the text on top of it. Then run simulated campaigns so the lesson has somewhere to land.
AI-generated Attacks and Deepfakes
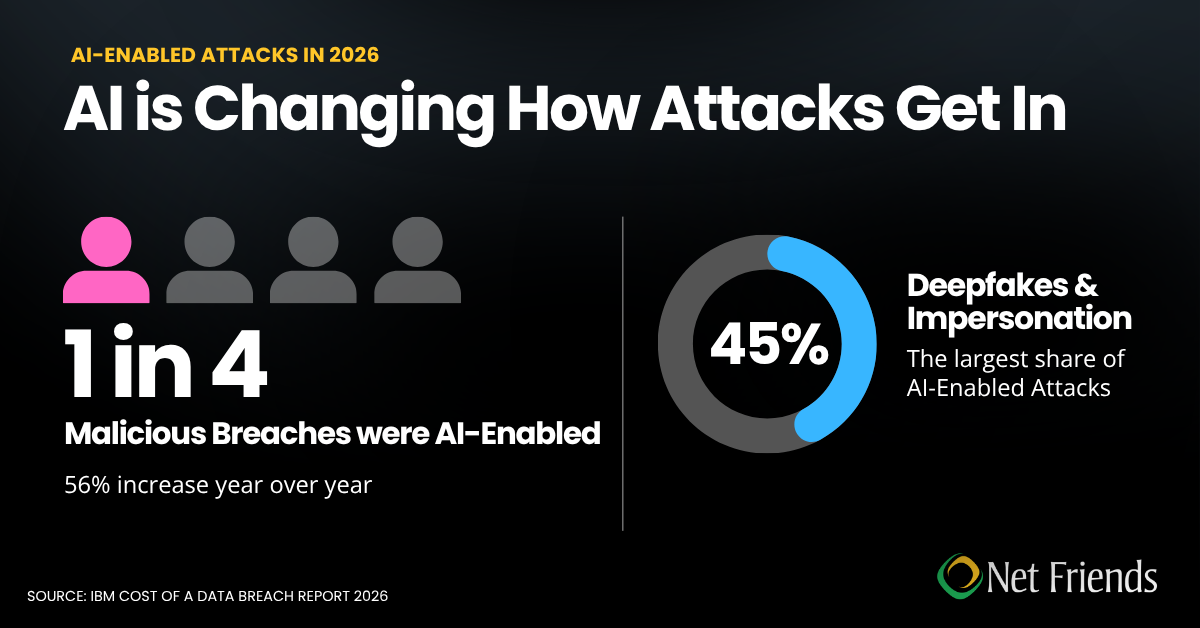
This is the topic that did not exist in most training decks three years ago and now belongs near the top. IBM reported that one in four malicious breaches were AI-enabled in 2026, a 56% jump year over year. Deepfake and impersonation attacks made up the largest share of them at 45%.
Practically, this means the old advice to watch for bad grammar is retired. AI writes clean, personalized, on-brand email at scale. It also clones voices from a few seconds of audio and puts a familiar face on a video call.
Train your team to verify high-stakes requests through a second, known channel. A phone call to a saved number beats trusting a voice on a call you did not initiate. Agree in advance that nobody will ever be punished for pausing a payment to confirm it.
Vishing and Help Desk Impersonation
Voice phishing works because phones feel personal. Callers pose as your bank, the IRS, Medicare, a vendor, or your own IT department, and they are patient.
Help desk impersonation deserves its spotlight. Attackers now call service desks pretending to be a locked-out employee, and they call employees pretending to be the service desk. IBM flagged both this pattern and MFA fatigue among the leading social engineering routes into organizations. Your training should cover how your real help desk verifies identity, and your help desk needs a verification standard strong enough to survive a convincing story.
Modern Password Practices
This one needs a real update, because a lot of training material still teaches rules that current guidance has retired.
Length now matters more than character soup. NIST recommends at least 15 characters when a password is the only factor. Organizations should not impose arbitrary composition rules, and they should not force periodic password rotation. Change a password when there is evidence of compromise, not because 90 days went by. Forced rotation just teaches people to add a 1 to the end.
Net Friends Pro-Tip: Check the strength of your password.
What should you teach instead? Long unique passphrases for every account, a password manager to hold them, screening against known breached password lists, and passkeys wherever the option exists. Passkeys are meaningfully harder to phish than anything you can type.
Multi-Factor Authentication
MFA is still one of the highest value controls you can deploy. It asks for a second proof of identity, so a stolen password stops being a skeleton key.
Important to remember, not all factors are equal. Teach people about MFA fatigue. If someone gets a flood of approval prompts they did not request, the answer is deny and report, not tap to make it stop.
Safe AI Use and Shadow AI
Your team is already using AI tools. The question is whether they are using approved ones. IBM found that shadow AI incidents doubled to 43% of all AI-related incidents, which tells you how quickly unsanctioned tools spread when nobody offers a sanctioned path.
Banning everything pushes usage underground, where you cannot see it. A better approach is a short, clear acceptable use standard. Name the approved tools. Say plainly what data must never be pasted into a public chatbot, including client records, credentials, source code, or a client contract. Explain that AI output needs a human review before it goes out the door. Then make the approved option genuinely good enough that people want to use it.
Devices, Browsing, and Working from Anywhere
Phones and laptops carry a startling amount of business data, and they leave the building every day. Cover screen locks and strong device passcodes, prompt patching of operating systems and browsers, care with app permissions and browser extensions, and the risks of public Wi-Fi and public charging ports.
Add a line about home networks while you are at it. Default router passwords are still one of the easiest wins available to anyone who wants in.
How to Make the Training Stick
Annual click through training checks a compliance box and changes very little. What works is shorter and more frequent. Run brief monthly modules instead of one long yearly session. Send phishing simulations continuously and use the results to coach rather than to shame. Tailor content by role, because your finance team faces different bait than your field technicians. Give leadership visible participation, since culture follows the org chart. And measure improvement in report rates, not just failure rates.
Let's Build Your Security Culture Together
NetSafe ID, our security awareness training pairs quality training with phishing simulations, so your staff has the knowledge to spot trouble. Ready to turn your team into your strongest control? Start a conversation with Net Friends and let's talk about what your training program needs next.
What to read next :
Social Engineering 101: Understanding Common Tactics
Do Passkeys Mean the End of Passwords?
How Multi-Factor Authentication (MFA) Secures Your Business Operations
5 Data Privacy Best Practices for AI Users

Take IT Off Your To-Do List.
Tech holding you back? Losing productivity to downtime?
Discover how we can simplify your tech and free up your time, contact us today.
At Net Friends, we believe in the power of human expertise. While we leverage AI to enhance our content and processes, all blog posts are written and edited by our knowledgeable staff. You can trust you are getting insights directly from our team.